
The public narrative surrounding India’s digital transition champions a frictionless, democratic leap into global technological supremacy. However, an empirical techno-legal audit of the actual ground reality reveals an acute, structural imbalance where rapid front-end digitization has outpaced backend cybersecurity architecture, forensic transparency, and institutional accountability. On the ground, the Indian state has deliberately rejected the European Union’s model of a centralized, overarching AI Act. Instead, the real-world strategy operates as a fractured “patchwork” ecosystem where the state avoids passing restrictive legislative statutes, opting instead to build technocratic constraints directly into system architectures while stretching legacy legal provisions to police digital infractions.
This dual-edged approach relies heavily on the Digital Personal Data Protection (DPDP) Act, 2023, as a proxy AI regulation. Because advanced artificial intelligence systems and agentic multi-agent frameworks depend entirely on the massive ingestion of behavioral and demographic data lakes, the Data Protection Board (DPB) functions on the ground as the primary adjudicator of AI development, penalizing data processing violations rather than AI logic itself. Supplementing this proxy framework is the Ministry of Electronics and Information Technology’s (MeitY) reliance on fast-tracked executive interventions via the IT Rules. These administrative modifications bypass traditional parliamentary debate to force immediate, platform-level liability for synthetically generated media, deepfakes, and automated algorithmic outputs.
The structural foundation of India’s techno-legal matrix is anchored to its expanding Digital Public Infrastructure (DPI), heavily reliant on centralized biometric databases and conditional access to basic rights. This architecture, frequently critiqued by independent legal observers as an Orwellian panopticon, enforces compliance through service denials and economic coercion, converting citizenship into a privilege that must be repeatedly authenticated. Essential citizen portals, such as the municipal e-governance systems operated by the Municipal Corporation of Delhi (MCD), expose severe vulnerabilities within this framework. On the ground, routine civic requests routinely devolve into exercises in bureaucratic attrition, where active citizen filings and certificate applications vanish from backend dashboards without explanation, only to reappear hours after formal grievances are escalated to senior authorities.
India’s digital transformation is marked by systemic challenges across administrative, cryptographic, and financial domains, where rapid technological deployment often outpaces institutional oversight and legal accountability.
Institutional Opacity And Cryptographic Vulnerabilities
Citizens and auditors frequently face obfuscation when demanding database logs from government portals, shielding internal actions from the Information Technology Act, 2000, and the Bharatiya Nyaya Sanhita, 2023. This administrative risk is compounded by foundational cryptographic weaknesses; for instance, a flaw in an internal Python key-generation script exposed weak private keys across multiple Certifying Authority certificates, leading to global browser trust revocations. Such gaps also affected judicial workflows when executive authorities acted upon fraudulent digital takedown orders featuring forged court seals and QR codes due to a lack of automated digital signature validation.
Financial Automation And API Exploitation
The financial sector faces targeted threats from AI-assisted penetration tools like Artex, which enabled threat syndicates to siphon funds via exploited settlement and Real-Time Gross Settlement (RTGS) interfaces, such as the ₹13.97 crore breach at the Central Bank of India. Smaller non-banking financial companies (NBFCs) have similarly lost hundreds of crores as attackers bypass Know Your Customer (KYC) checks and loan limits by hijacking payout APIs. These technical vulnerabilities are frequently compounded by physical branch and insider control failures, highlighting the limits of static perimeter defenses.
Surveillance Capitalism And CBDC Pilots
The concentration of biological and behavioral data within state repositories fuels large-scale profiling and self-censorship, with marginalized communities suffering disproportionate authentication failures in biometric systems. This state-led architectural control extends to trials of the retail Central Bank Digital Currency (e-Rupee), which introduces programmable limits on currency—such as expiration dates or merchant restrictions—that challenge traditional economic anonymity. In response, parts of the informal economy have initiated a “digital U-turn,” shifting back to cash-only transactions to retain financial privacy.
Constitutional Pressures And Techno-Legal Remedies
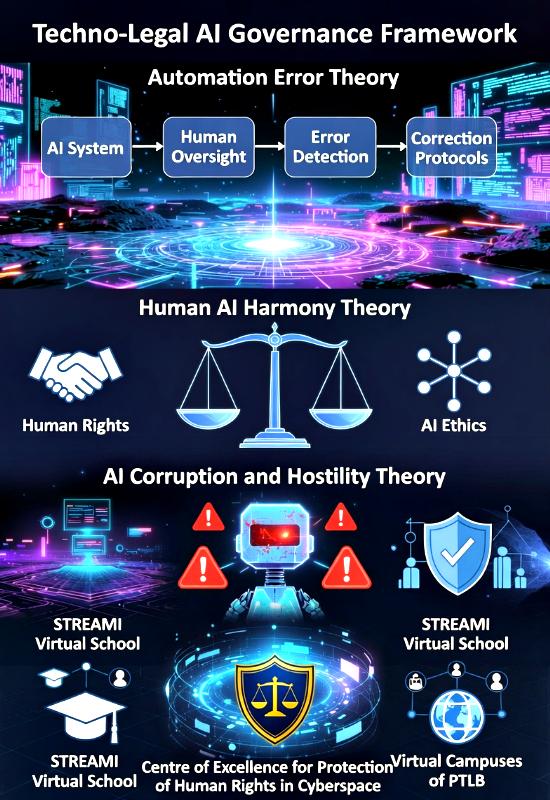
Interception powers under Section 69 of the IT Act operate without independent judicial warrants, a structural opacity underscored during privacy controversies like Pegasus. To address the chasm between rapid digital deployment and legal liability, India pioneered interdisciplinary “Techno-Legal Specialists” through the Perry4Law Organisation (Sovereign P4LO/PTLB) starting in 2002. This model promotes human-centric governance frameworks, continuous adversarial testing, and Zero-Trust Architectures to align technological scale with constitutional safeguards.